
Salesforce Encryption
Customer and opportunity data stay useful in Salesforce, without giving the CRM the last encryption key.
PKI & Certificates Management
Issue, renew and retire machine and workload identities without spreadsheet PKI or surprise outages.
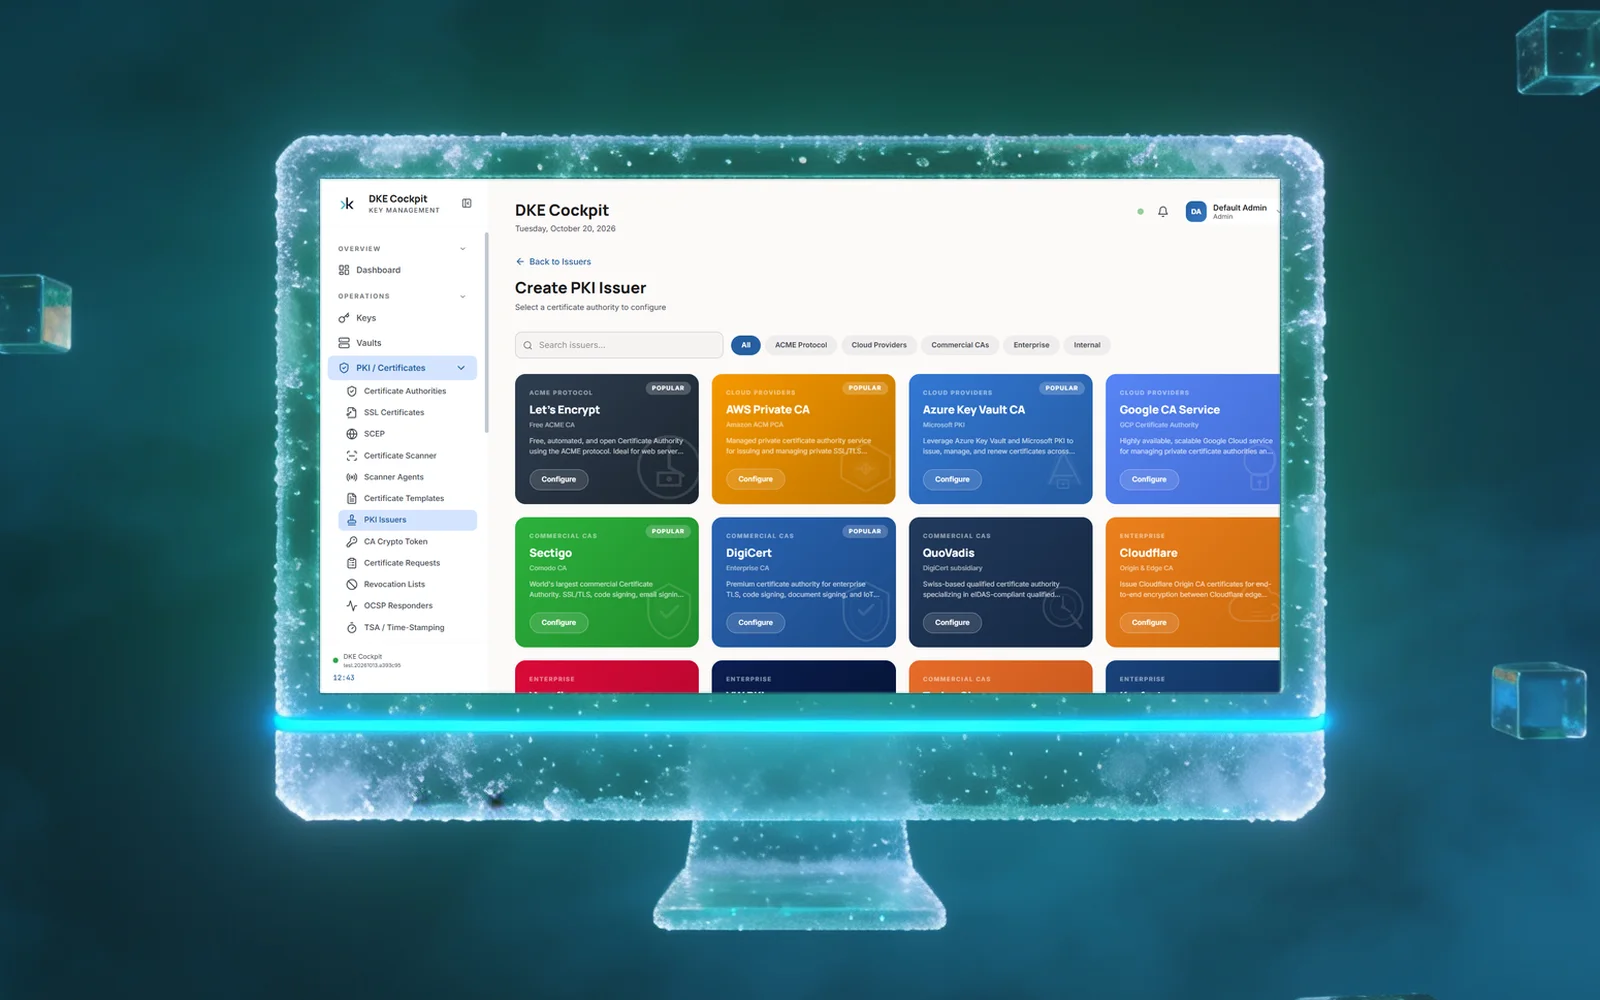
Issue, renew, deploy and revoke every machine identity from private, public and cloud CAs, with CA keys that stay in your vault, HSM or MPC cluster.
Expiry alerts by e-mail, Teams, Slack or webhook, and ACME renewal information so clients renew on time as lifetimes shrink towards 47 days.
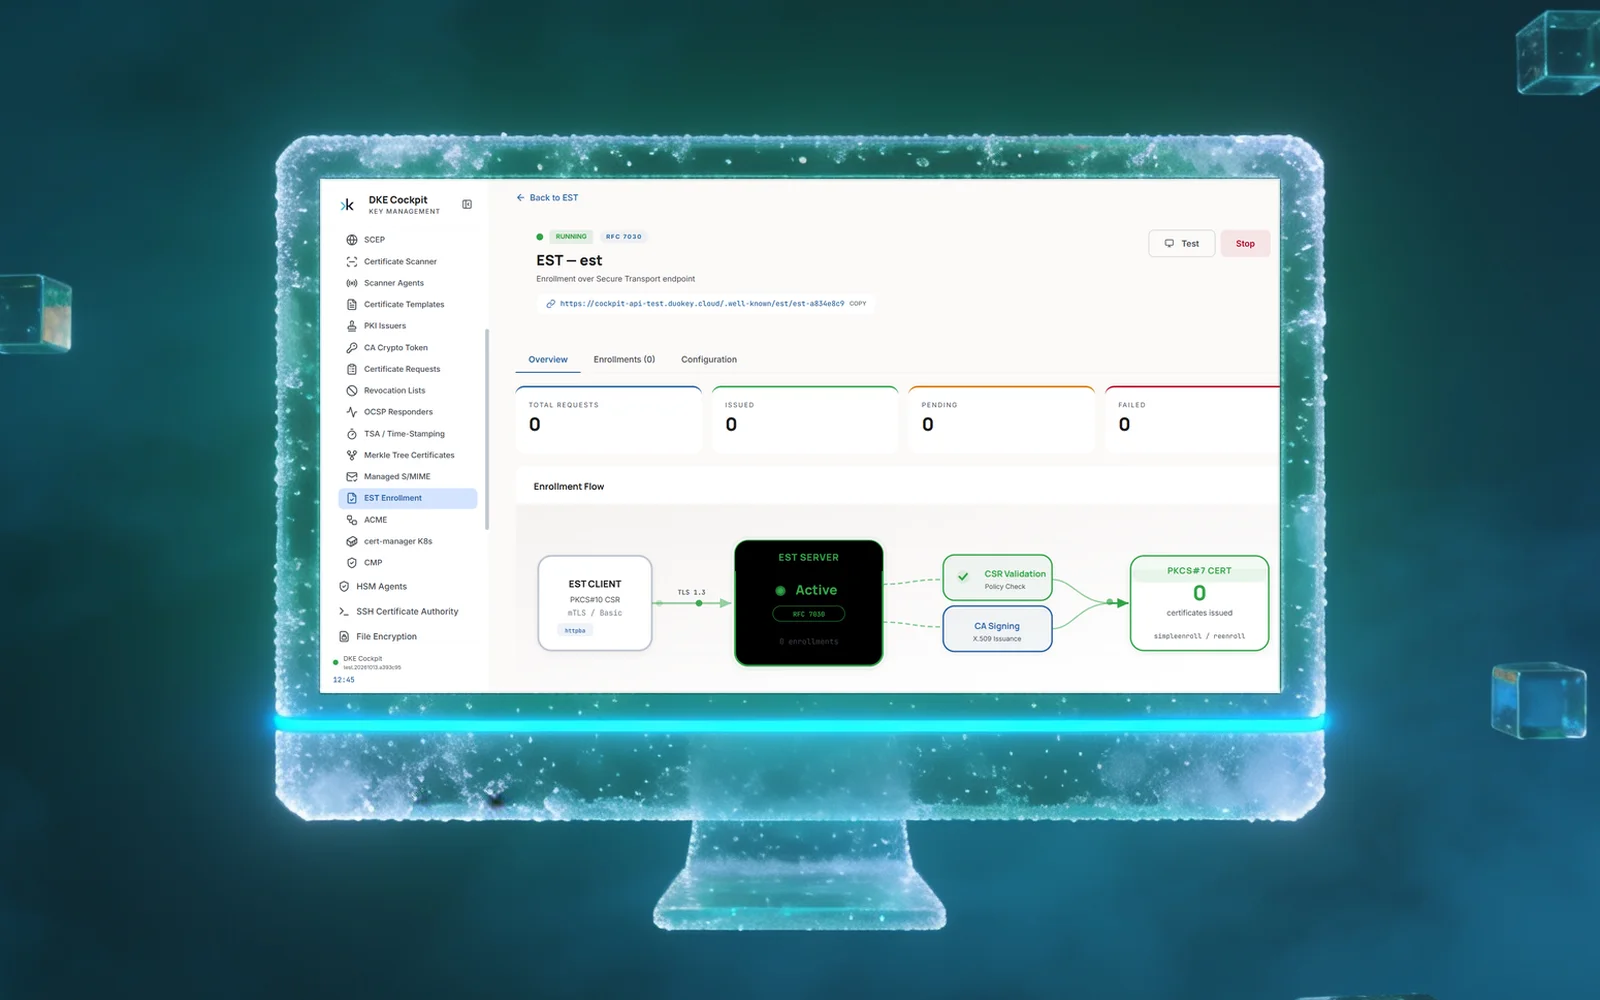
ACME, EST, SCEP, CMP and Kubernetes cert-manager give developers and devices certificates without a ticket.
M-of-N quorum on CA changes and revocation, access policies on every enrolment protocol, and CA keys that are never exported.
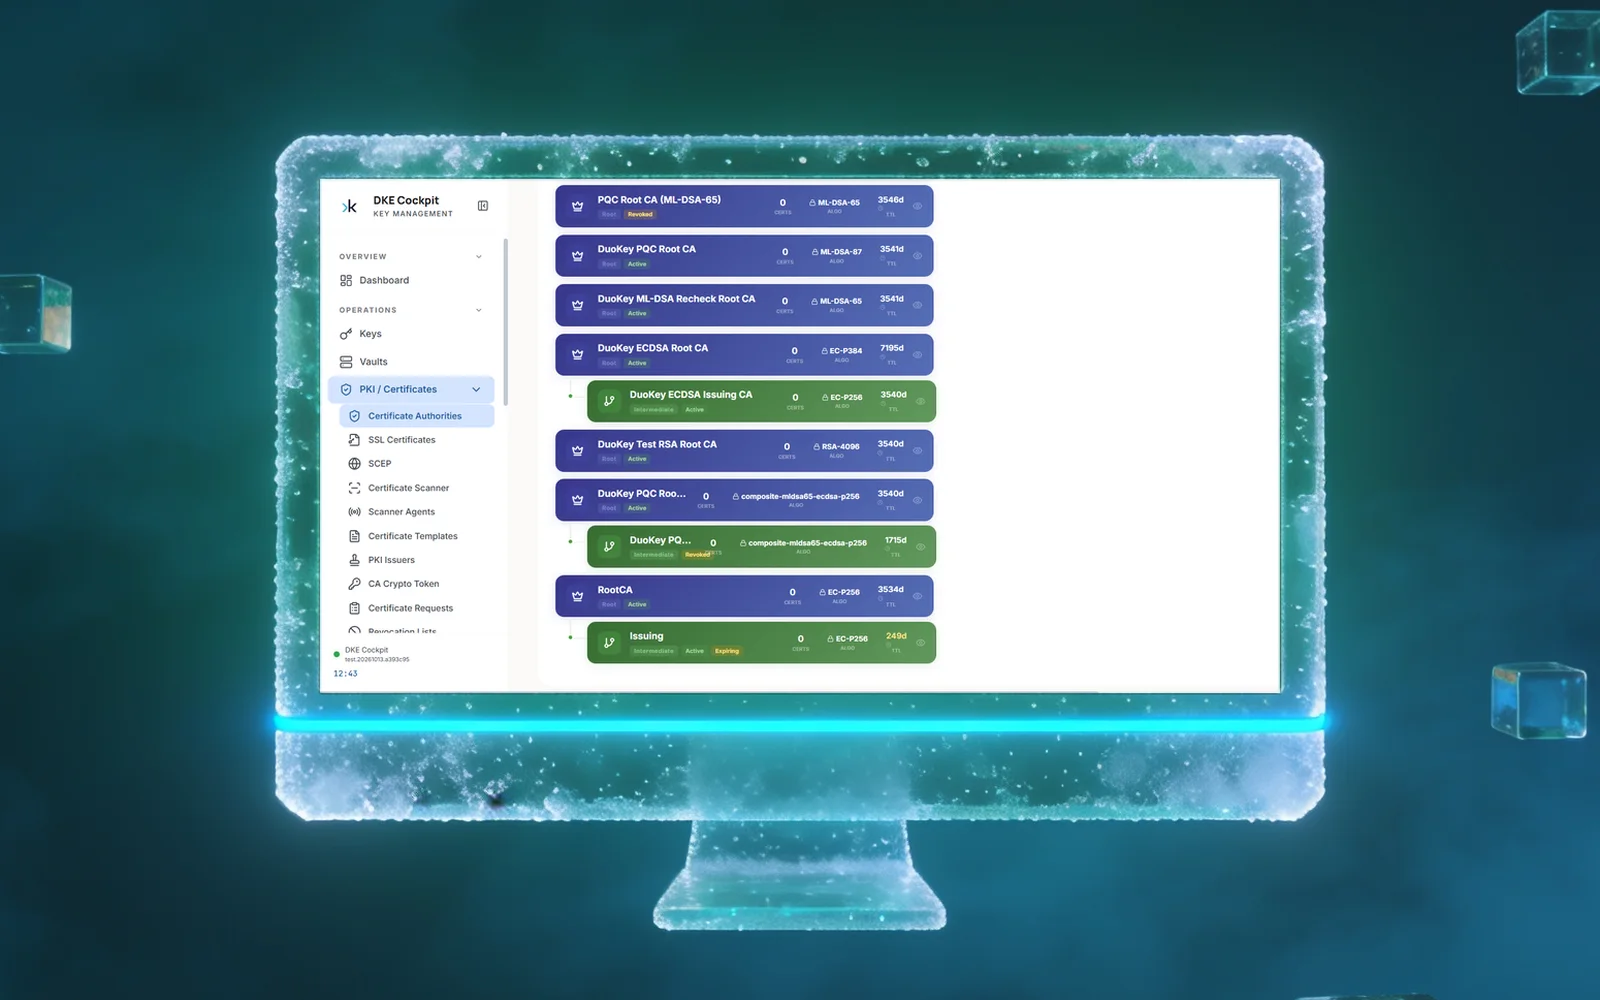
Run root and intermediate CAs on classical or post-quantum algorithms, and front the public and cloud CAs you already use, from one console.
Servers, devices, MDM and Kubernetes clusters enrol with the protocol they already speak, each endpoint bound to the CA you choose.
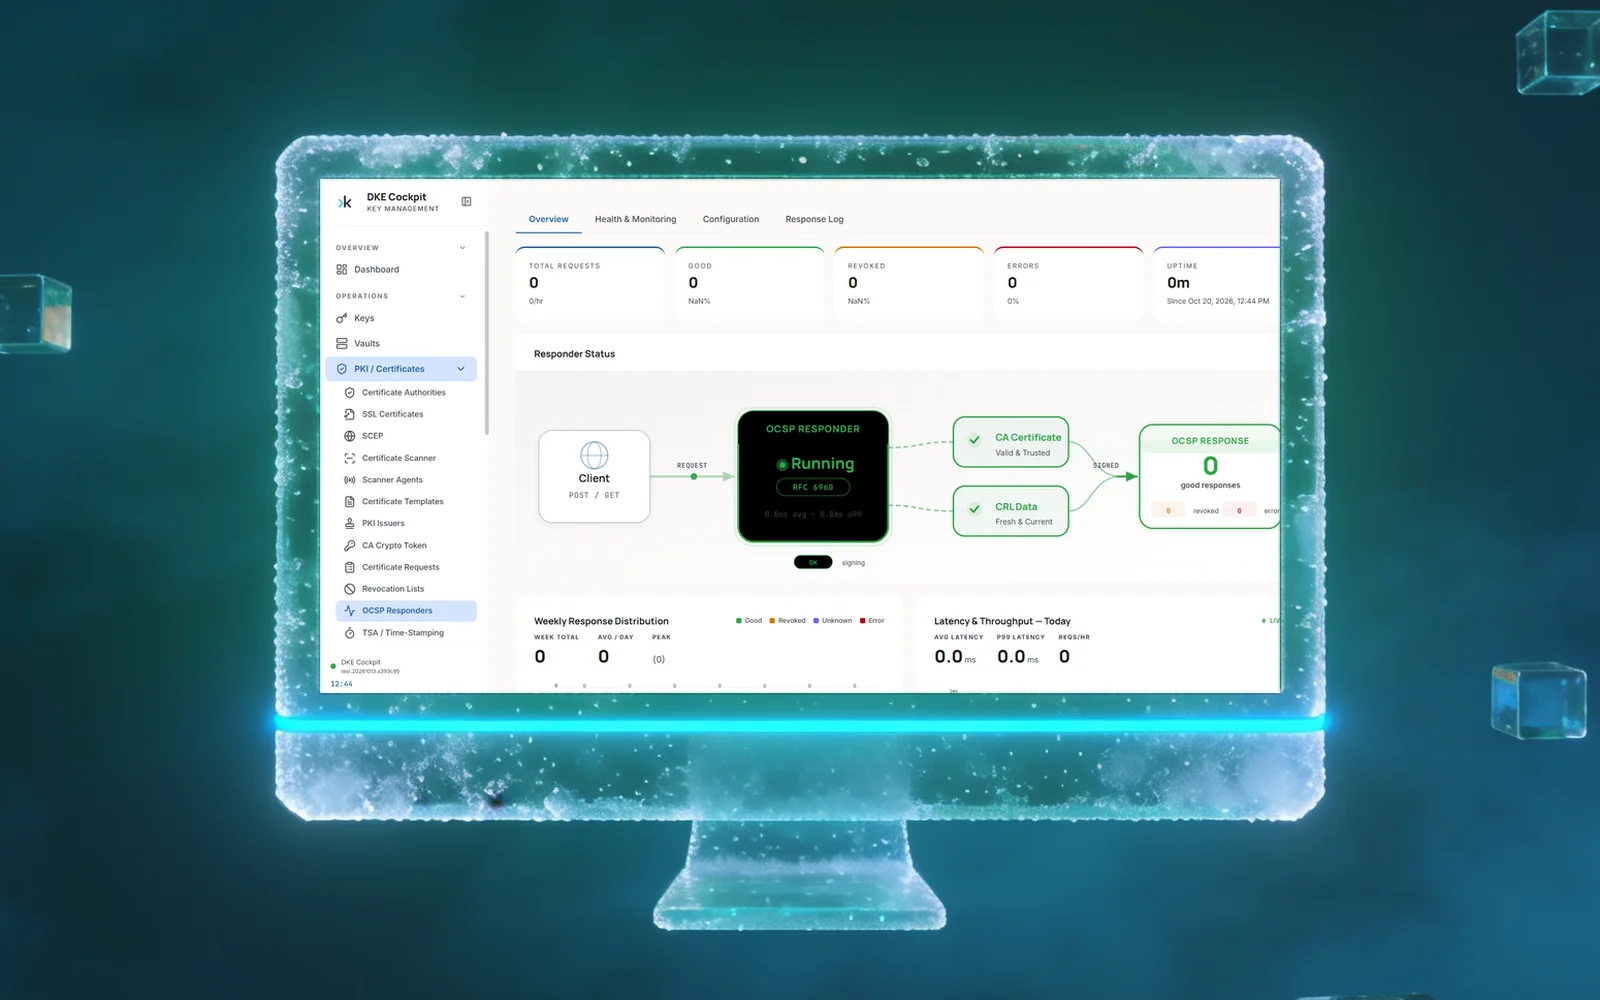
Per-CA OCSP responders and CRL distribution let gateways, browsers and back-ends refuse a revoked certificate the moment it is revoked.
A CA created with a vault signs every certificate, CRL and OCSP response in that vault: an HSM, a cloud KMS or an MPC cluster. Nothing is exported.
Pick the target and the Cockpit deploys the certificate, validates it, rolls back on failure, then renews and redeploys before expiry.
Suspend, reactivate, cascading revoke and archive, with an impact preview before any cascading action.
Reusable templates and a CSR approval workflow: request, approve or reject, issue.
Network and agent-based TLS scanning, discovered-certificate import, Mozilla, NIST and PCI DSS checks.
ML-DSA and SLH-DSA issuance and a hybrid composite for staged migrations.
SignTool, JAR, Git and cosign signatures with non-exportable vault keys and approvals.
EST and CMP provisioning for IoT and network fleets, in production at Volkswagen.
Run the same Cockpit as a service, in your own data centre, or both, with CA keys wherever your policy requires.
Proof in practice
Deep dives
Compliance
Trust
Customer programmes
Talk to us about private CAs, ACME automation and post-quantum certificates.
Products
Customer and opportunity data stay useful in Salesforce, without giving the CRM the last encryption key.