DuoKey

Agentic Crypto Agility

Give every AI agent a cryptographic identity it can prove

Autonomous agents now request keys, sign transactions and touch production data faster than any human review cycle. DuoKey issues, rotates and revokes agent credentials automatically, so security keeps pace with automation.

Inside the Cockpit

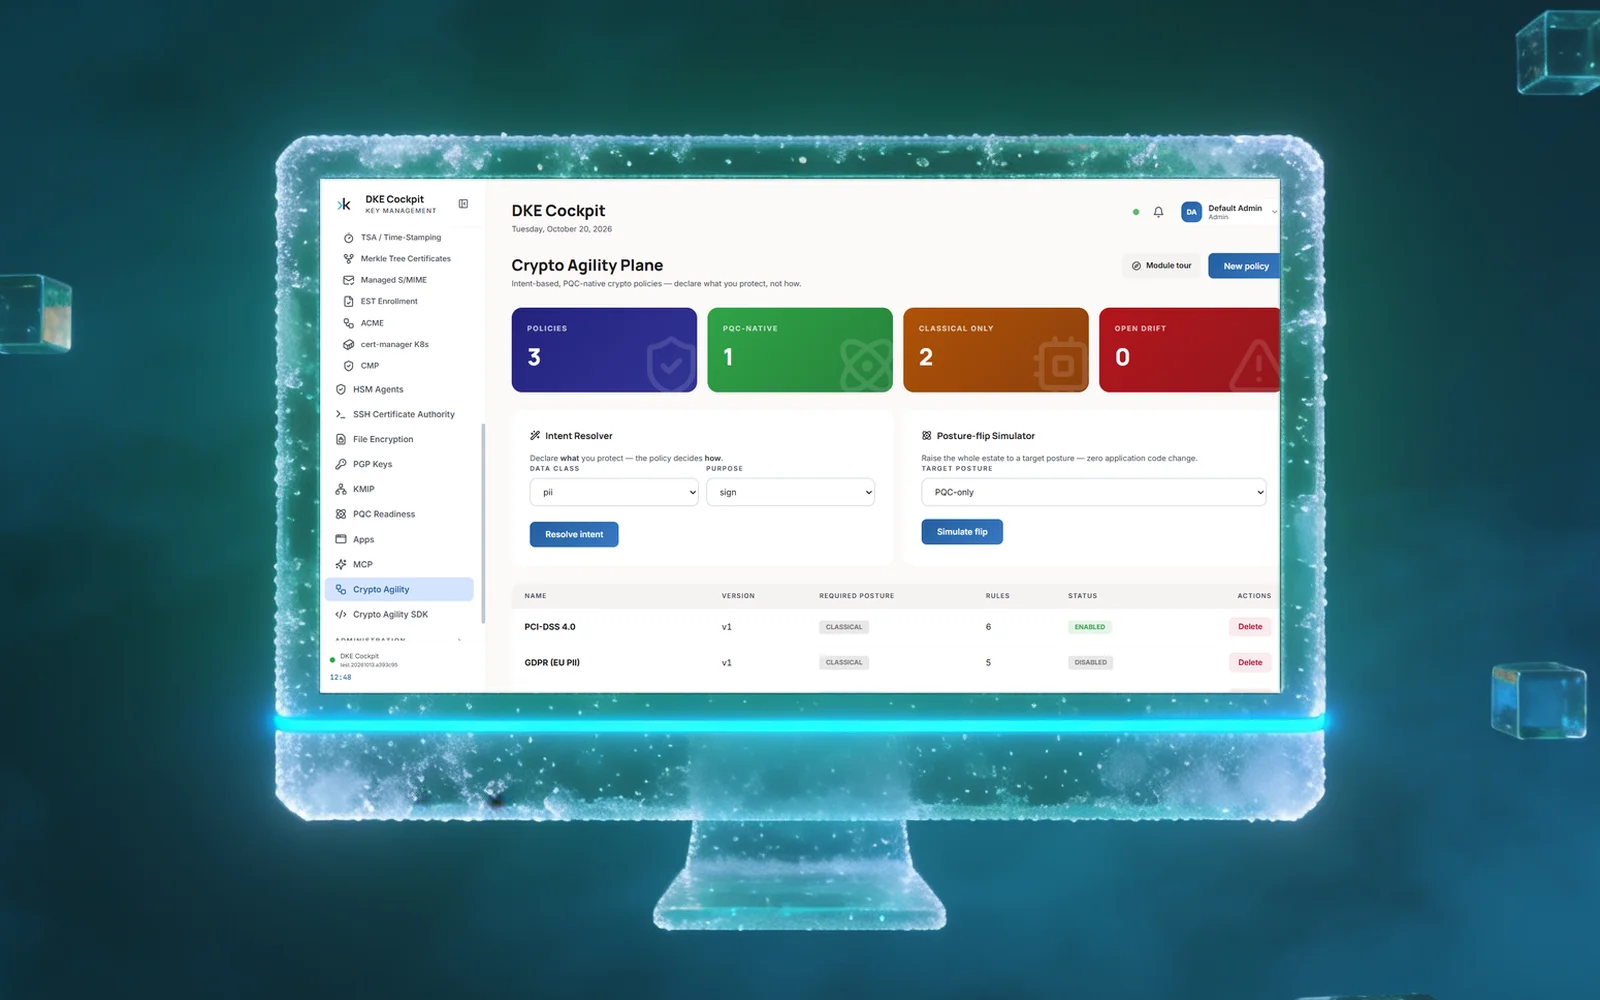
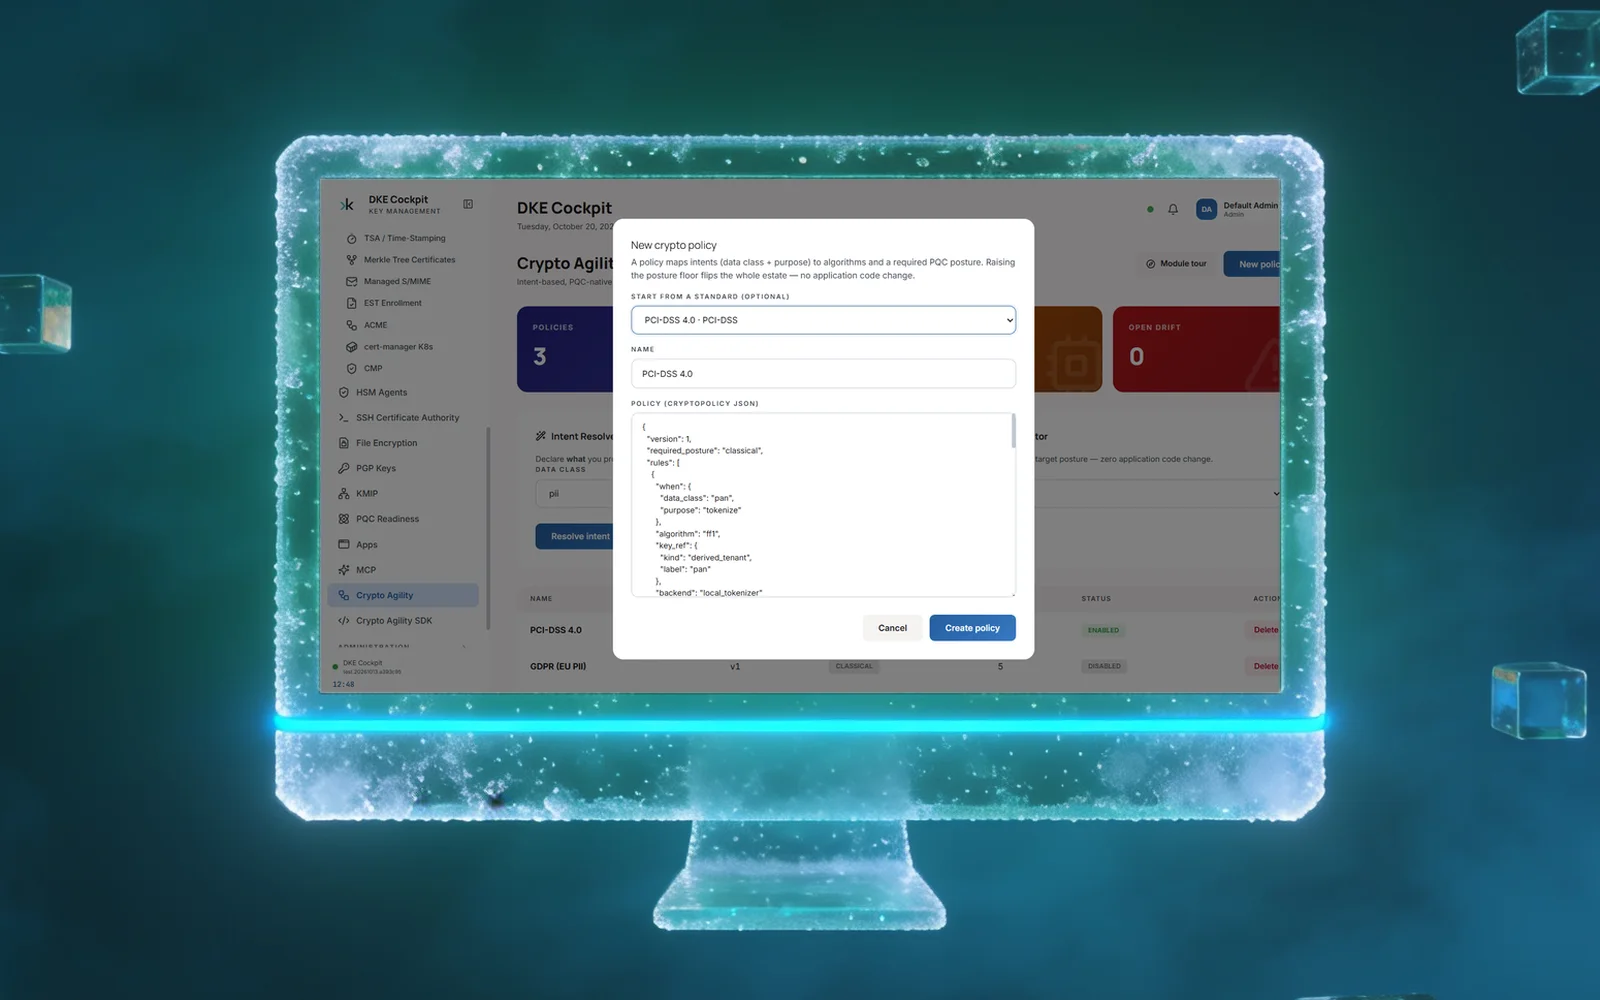
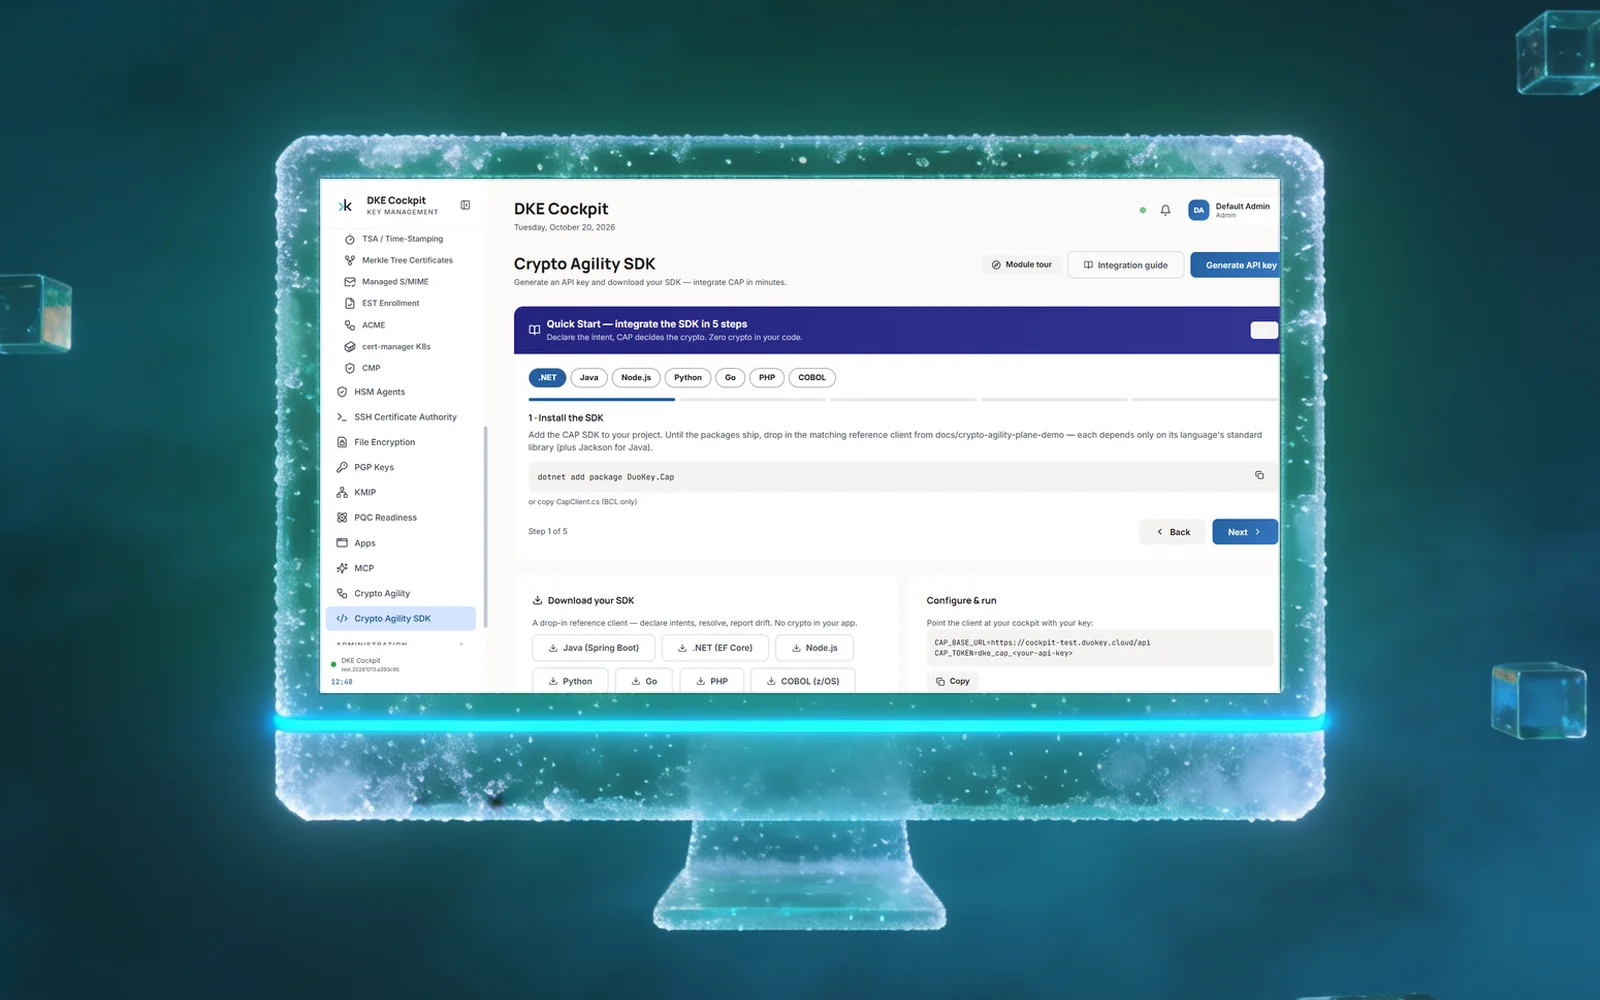
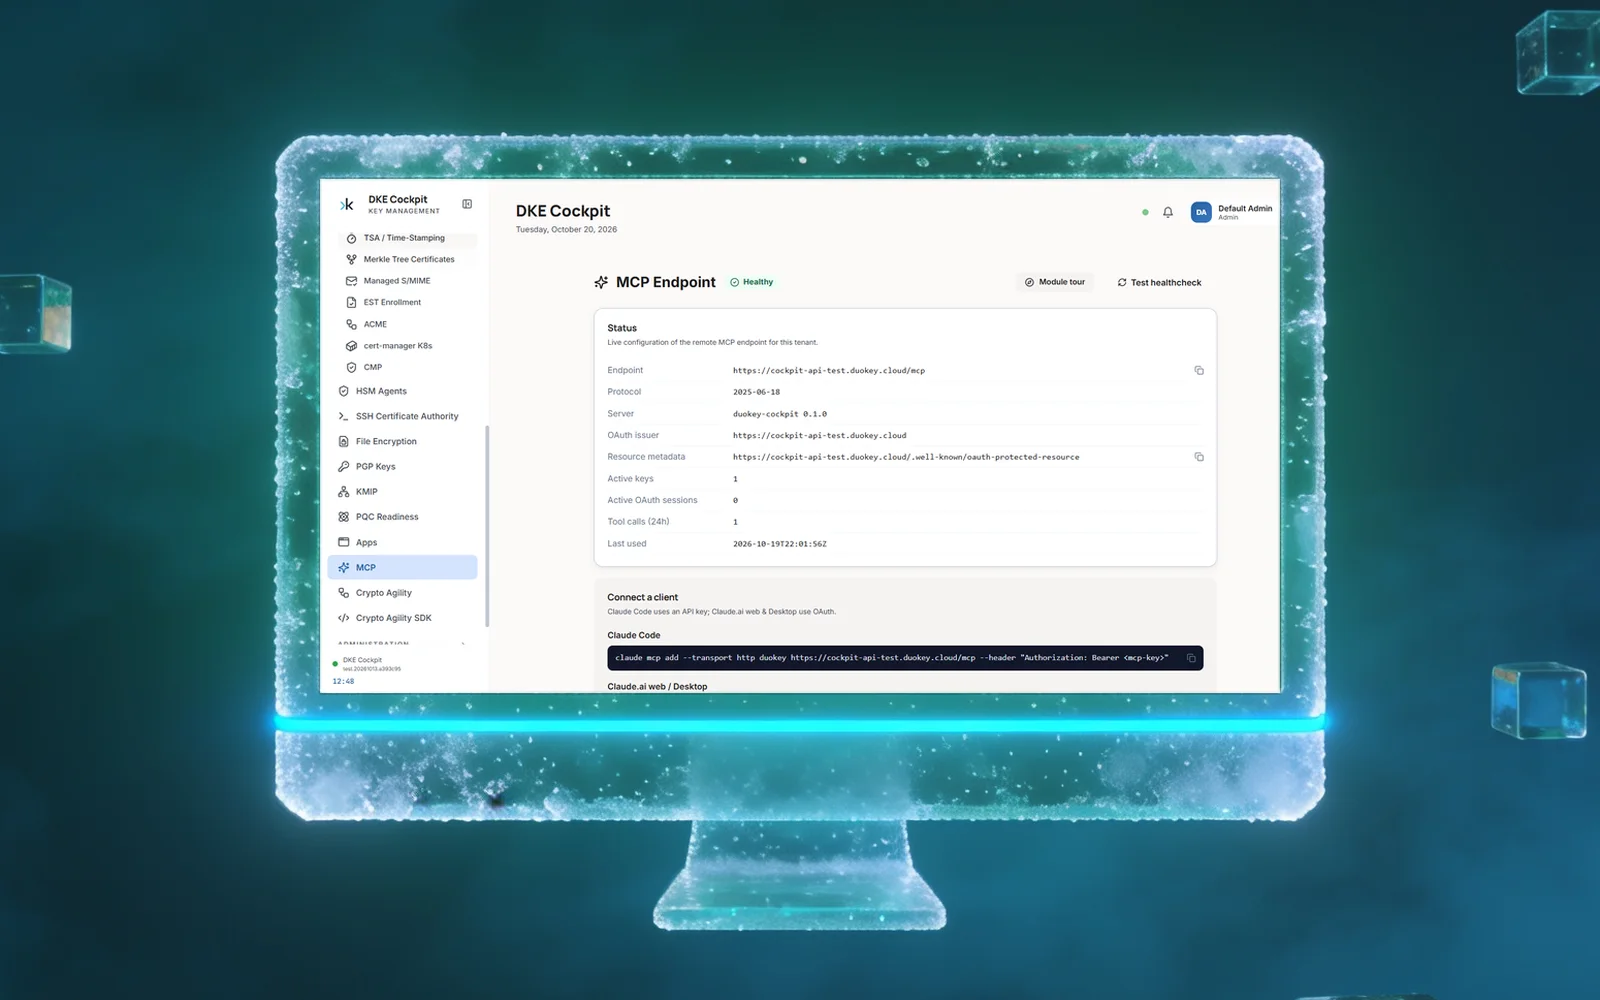
Declare intent. Let policy decide the cryptography.

DuoKey Cockpit crypto agility plane with policies, intent resolver and posture-flip simulatorDuoKey Cockpit new crypto policy started from the PCI DSS 4.0 standardDuoKey Cockpit Crypto Agility SDK quick start with .NET, Java, Node.js, Python, Go, PHP and COBOL clientsDuoKey Cockpit MCP endpoint status and client connection instructions

Agility plane

Give every AI agent

An identity it can prove. DuoKey issues, rotates and revokes agent credentials automatically, so security keeps pace with automation.

Know your agent

A cryptographic identity issued per agent at creation.

Revoke one, not all

Unit revocation without fleet-wide credential rotation.

Accountable

A full audit trail from crypto change to accountable human.

An identity for every agent, at birth.

Each agent receives its own cryptographic identity when it is created, instead of borrowing a shared service credential.

  • Access scoped to task and owner.
  • No standing shared roles.

Revoke the agent, not the fleet.

When one agent misbehaves or is retired, revoke its identity alone; every other agent keeps working.

  • No fleet-wide credential rotation.
  • Other agents are not affected.

Agents act within guardrails.

Agents manage renewals and rotations themselves, under policies that bound what they may change, and sign attestations of sensitive actions.

  • Signed attestation of sensitive actions under policy.
  • Declare intent; policy decides the algorithm.

Every action leads to a human.

The audit trail connects each cryptographic change made by an agent to the human who owns it.

  • Evidence for DORA, NIS2 and AI governance reviews.
  • MCP tools for agents, the Cockpit for humans.

Two use cases

Identity for agents. Autopilot for the estate.

Autonomous software creates two security problems at once: nobody can say which agent acted and the cryptography underneath cannot keep up with machine speed.

DuoKey answers both with one platform, agents get provable identities and the keys and certificates they use stay current under policy.

Use case 1

Manage the cryptographic estate with agents

Let agents run renewals, rotations and revocations under guardrails.

Certificates expire, algorithms change and key material drifts out of policy faster than a manual program can follow. DuoKey agents prepare the work, scan what is due, propose the change, execute what policy allows, while people approve the exceptions.

  • Agents surface expiring certs, weak algorithms and policy drift
  • Routine renewals and rotations run automatically within guardrails
  • Every crypto change is logged against the agent that executed it
CA

Crypto Agent

Live

Use case 2

Add cryptographic identity to agents

Issue every agent credentials only it can use and prove.

Shared service accounts erase accountability. DuoKey gives each agent, script and pipeline its own cryptographic identity at creation, bound to an owner, scoped to a task and revocable the moment context changes.

  • One cryptographic identity per agent, no copied secrets
  • Access scoped to task and owner, not a standing role
  • Immediate revocation when an agent is retired or misbehaves

The problem

Agents need identity and crypto ops at machine speed

Shared credentials and manual key programs cannot keep up.

Autonomous agents request keys, sign transactions and touch production data faster than any human review cycle. Without per-agent identity, audit trails dead-end at a shared account. Without agent-driven crypto ops, certificates and keys fall out of policy before anyone notices.

  • Shared service accounts

    Ten agents on one credential, no log can name the actor.

  • Manual crypto programs

    Renewals and rotations lag behind fleets that scale by the hour.

  • Standing access

    Permissions outlive the task they were issued for.

  • No provable owner

    Incident response starts with a guess, not a cryptographic proof.

What changes

Security that keeps pace with automation

Know your agent: every agent gets a revocable cryptographic identity; no shared service account carries production access; every sensitive action can be attested to a named principal.

  • Cryptographic identity issued per agent at creation (know your agent)

  • Unit revocation without fleet-wide credential rotation

  • Signed attestation of sensitive actions under policy

  • Agents manage renewals and rotations under guardrails

  • Access scoped to task and owner, not standing shared roles

  • Full audit trail from crypto change to accountable human

Security leadership

What the board is asking

Agentic Crypto Agility

Four questions surface in every security review.

Talk to our security architects

Trust

Assurance and customer programmes

Customer programmes

Autonomous agents, accountable cryptography.

See agents receive, rotate and lose their identities under policy, in your own environment.